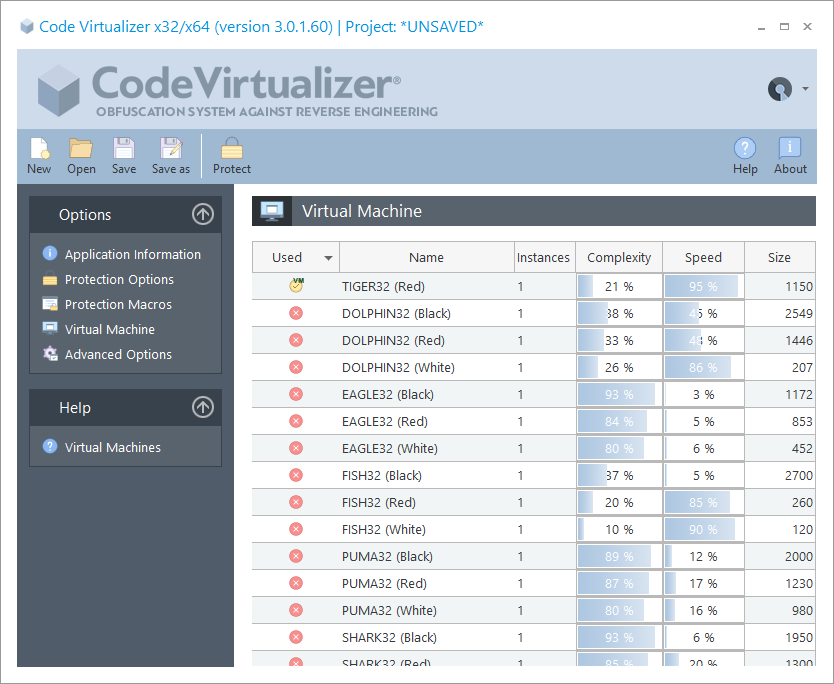
Code Virtualizer 4.0 beta
- [+] Improved VIRTUALIZER_END macro destruction with varied architecture-specific safe randomized instructions
- [!] Fixed ELF protection of binaries requiring 16 KB load-segment alignment
- [!] Fixed x64 MinGW/GCC protection failures when cleanup-only inline GNU LSDA metadata is used by virtualized exception handling
- [!] Fixed x64 protection failures in functions with large stack frames or arrays when valid GS cookie offsets coincided with readable image RVAs
- [!] Fixed ARM64 VM boundary handling of X18 for Windows and ELF Shadow Call Stack binaries
- . . .